The ICrypto class, This is base interface that provide encryption functionality. More...
#include <icrypto.h>
Public Types | |
| enum | Features { Signing = 0x01 , Encryption = 0x02 } |
| The Features enum this is list of the supported description features. More... | |
Public Member Functions | |
| bool | makeKeys (QByteArray &pubKey, QByteArray &privKey) const |
| makeKeys This method generate the public and private keys of the ECDSA. | |
| virtual QSsl::KeyAlgorithm | keyAlgorithm () const =0 |
| keyAlgorithm This method should be return Qt Key algorithm (needed for generate cetrificates.) | |
| virtual Features | supportedFeatures () const =0 |
| supportedFeatures This method should return supported featurs of the current encryption algorithm | |
| virtual QByteArray | decrypt (const QByteArray &message, const QByteArray &key)=0 |
| decrypt This method decrypt message using key. | |
| virtual QByteArray | encrypt (const QByteArray &message, const QByteArray &key)=0 |
| encrypt This method encrypt message using key. | |
| virtual QByteArray | signMessage (const QByteArray &message, const QByteArray &key) const =0 |
| signMessage This method should be sign the message using the key. | |
| virtual bool | checkSign (const QByteArray &message, const QByteArray &signature, const QByteArray &key) const =0 |
| checkSign This method should be check signature of the message using the key. | |
| virtual void * | makeRawKeys () const =0 |
| makeKeys This method generate the public and private keys of the ECDSA. | |
Detailed Description
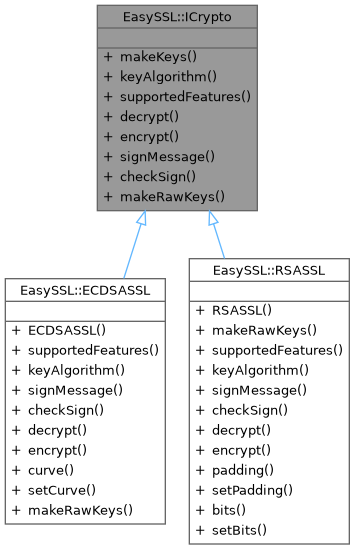
The ICrypto class, This is base interface that provide encryption functionality.
Member Enumeration Documentation
◆ Features
Member Function Documentation
◆ checkSign()
|
pure virtual |
checkSign This method should be check signature of the message using the key.
- Parameters
-
message This is input data that should be decrypted. signature This is signature that will be checked for the message. key This is a public key for encryption the inpputData.
- Returns
- decrypted data array.
- See also
- AsyncKeysAuth::encrypt
Implemented in EasySSL::ECDSASSL, and EasySSL::RSASSL.
◆ decrypt()
|
pure virtual |
decrypt This method decrypt message using key.
- Parameters
-
message This is encrypted message that should be decrypted. key This is key that will be used for decryption for the message.
- Returns
- decrypted message or empty string if method not supported or decrypted failed.
- See also
- IAsyncEncryption::encrypt
Implemented in EasySSL::ECDSASSL, and EasySSL::RSASSL.
◆ encrypt()
|
pure virtual |
encrypt This method encrypt message using key.
- Parameters
-
message This is a message that should be decrypted. key This is key that will be used for encryption for the message.
- Returns
- decrypted message or empty string if method not supported or decrypted failed.
- See also
- IAsyncEncryption::encrypt
Implemented in EasySSL::ECDSASSL, and EasySSL::RSASSL.
◆ keyAlgorithm()
|
pure virtual |
keyAlgorithm This method should be return Qt Key algorithm (needed for generate cetrificates.)
- Returns
Implemented in EasySSL::ECDSASSL, and EasySSL::RSASSL.
◆ makeKeys()
| bool EasySSL::ICrypto::makeKeys | ( | QByteArray & | pubKey, |
| QByteArray & | privKey | ||
| ) | const |
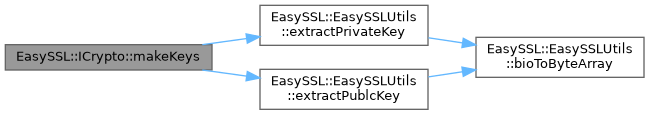
makeKeys This method generate the public and private keys of the ECDSA.
- Parameters
-
pubKey This is result public key. privKey This is result private key.
- Returns
- true if keys generated successful.
Definition at line 16 of file icrypto.cpp.
◆ makeRawKeys()
|
pure virtual |
makeKeys This method generate the public and private keys of the ECDSA.
- Returns
- pointer to generated keys. This method must return EVP_PKEY* structure.
Implemented in EasySSL::ECDSASSL, and EasySSL::RSASSL.
◆ signMessage()
|
pure virtual |
signMessage This method should be sign the message using the key.
- Parameters
-
message This is input data that should be signed. key This is a privete key for encryption the message.
- Returns
- signature data array.
- See also
- AsyncKeysAuth::descrupt
Implemented in EasySSL::ECDSASSL, and EasySSL::RSASSL.
◆ supportedFeatures()
|
pure virtual |
supportedFeatures This method should return supported featurs of the current encryption algorithm
- Returns
- Features list.
- See also
- Features
Implemented in EasySSL::ECDSASSL, and EasySSL::RSASSL.
The documentation for this class was generated from the following files:
- src/lib/src/public/easyssl/icrypto.h
- src/lib/src/public/easyssl/icrypto.cpp